
A Small AI Canary Release Can Still Trigger an Irreversible Business Action
AI canary deployment risk rises when a small share of production traffic can still trigger high-impact or irreversible actions. See how shadow testing, staged execution authority, action-level telemetry and consequence budgets can separate traffic exposure from the authority a new AI release is allowed to exercise.

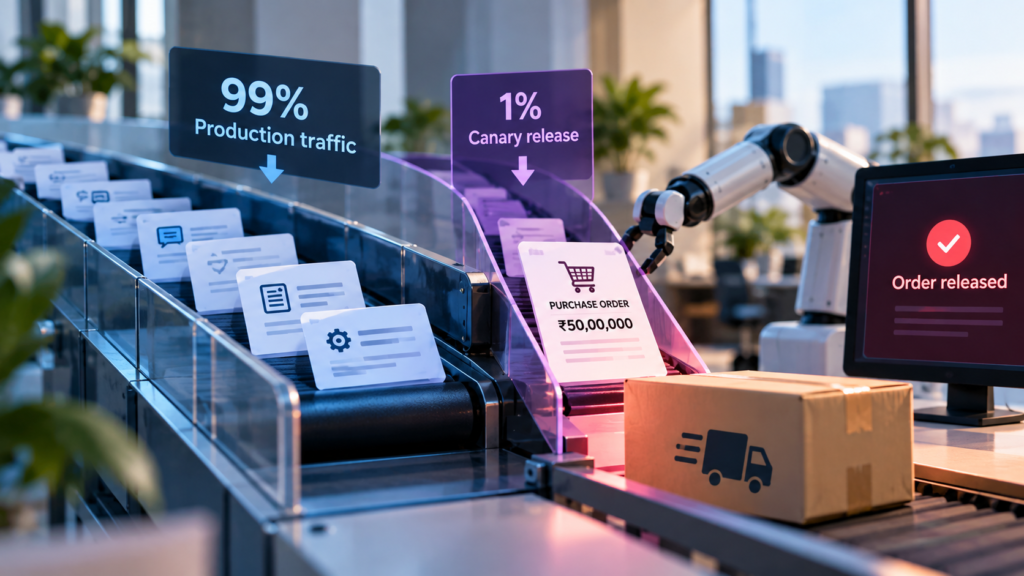
An AI canary deployment can restrict a new release to a tiny share of production traffic without restricting what that release is allowed to do. For systems that can act, rollout safety therefore depends on consequence as well as traffic percentage.
A new procurement-agent release receives 1% of production traffic. The rollout team considers the exposure small. The first two requests are routine, but the third creates a purchase order worth ₹50 lakh and releases it to a supplier.
Only a small fraction of traffic reached the new release. The problem is that one request was enough.
AI canary deployment limits frequency, not consequence
Canary rollout is designed to reduce exposure while a new deployment proves itself under live conditions.
Amazon SageMaker AI, for example, can send a small portion of endpoint traffic to a new fleet during a baking period. If configured CloudWatch alarms trip, traffic can be rolled back to the previous fleet through its deployment guardrails.
Azure Machine Learning supports a similar rollout progression: deploy the new version, test it, mirror production traffic, allocate a small percentage of live traffic and only then move all traffic.
For predictive services, limiting traffic can reduce the number of users exposed to a bad model. An acting AI system introduces another variable: the requests inside that percentage may carry very different consequences.
A request that drafts a supplier summary and a request that releases a purchase order both count as one request in the traffic split.
Operationally, they are not comparable units of risk.
The first live cases may be the ones that matter most
A canary receives a portion of whatever production work arrives. That means an unusual but consequential case can appear early.
A payments agent receiving 2% of requests might encounter a high-value transfer before it processes enough routine transactions to establish a reassuring error rate. A customer-service agent could receive an account-closure request, while a procurement agent might encounter the first order that crosses a financial approval threshold.
This complicates rollout judgments based mainly on aggregate measures such as request failures, latency, error counts or average task success.
A release can look healthy across ninety-nine low-consequence tasks and still behave incorrectly on the hundredth task that changes something difficult to reverse.
Shadow traffic and live canary traffic test different things
Azure’s rollout model makes a useful distinction between mirrored and live traffic.
With mirrored traffic in Azure Machine Learning, requests are copied to the new deployment, but clients continue receiving results from the existing deployment. Microsoft describes this as a way to collect metrics and logs without affecting client results.
For an AI application capable of external action, that creates a useful intermediate state.
A shadow deployment can evaluate a production request, select a hypothetical tool or propose an action without committing the result to the business system. Live canary traffic introduces real execution.
Once the new release can invoke tools, write records or issue instructions, rollout design has to govern more than which requests reach it.
Canary authority can expand separately from canary traffic
Traffic does not have to be the only thing that increases gradually.
An early production stage might allow the new release to read live data, retrieve production context, generate recommendations, propose tool calls and record what it would have done.
The next stage could permit low-consequence, reversible actions. Higher-consequence actions could remain behind human approval or continue to be executed by the previous production version until the new release has produced enough evidence on the relevant task class.
Full execution authority can come later.
The percentage of traffic and the percentage of authority no longer have to move together.
That gives rollout teams a way to expose the new system to real production conditions without granting every capability intended for steady-state operation on day one.
The important canary boundary may be the maximum permitted effect
Consider the ₹50 lakh purchase order again.
The more useful control is not simply whether the new release receives the request, but what it is permitted to commit when it does.
Purchase orders below a defined threshold might proceed automatically, while higher-value orders could be generated but held for approval. Changes to supplier bank details might remain disabled. Customer communications might be permitted while account termination is not.
The exact categories will differ by application, but the rollout question becomes more precise:
What is the maximum consequence one canary request is allowed to create?
That boundary can reflect financial value, reversibility, customer impact, legal significance, security sensitivity or the authority of the external system being changed.
Canary metrics should include what the system actually did
AWS canary deployment guardrails use monitoring alarms during canary and baking periods to decide whether rollout should continue or traffic should return to the old fleet.
For an acting AI system, useful rollout telemetry can extend beyond infrastructure and inference quality.
The team may need to know how many actions were proposed, how many were committed, which action classes were exercised, how often humans overrode them and whether the release entered capability categories that were expected to remain unused.
One incorrect action among a thousand requests may be acceptable in one workflow and disqualifying in another. The relevant signal comes from the action and its consequence, not from request count alone.
Safe rollout needs a consequence budget
Traffic splitting remains useful because it creates an observation period and limits the amount of production work handled by the new release.
For systems that can act, the canary stage can also carry a consequence budget.
That budget might take the form of transaction-value ceilings, a restricted tool set, mandatory approval for specific actions or a temporary prohibition on irreversible operations.
The rollout then expands along two dimensions: how much production work the release sees, and how much production authority it can exercise.
That makes canary deployment more than a percentage dial. It becomes a controlled expansion of what the new release is trusted to do.