
An Agent’s Memory Can Outlive the Permission That Created It
AI agent memory permission expiry creates a gap between source access and persistent memory. Learn how authorization lineage, recall eligibility and retention controls can prevent temporary access from creating an unlimited right to reuse stored information.

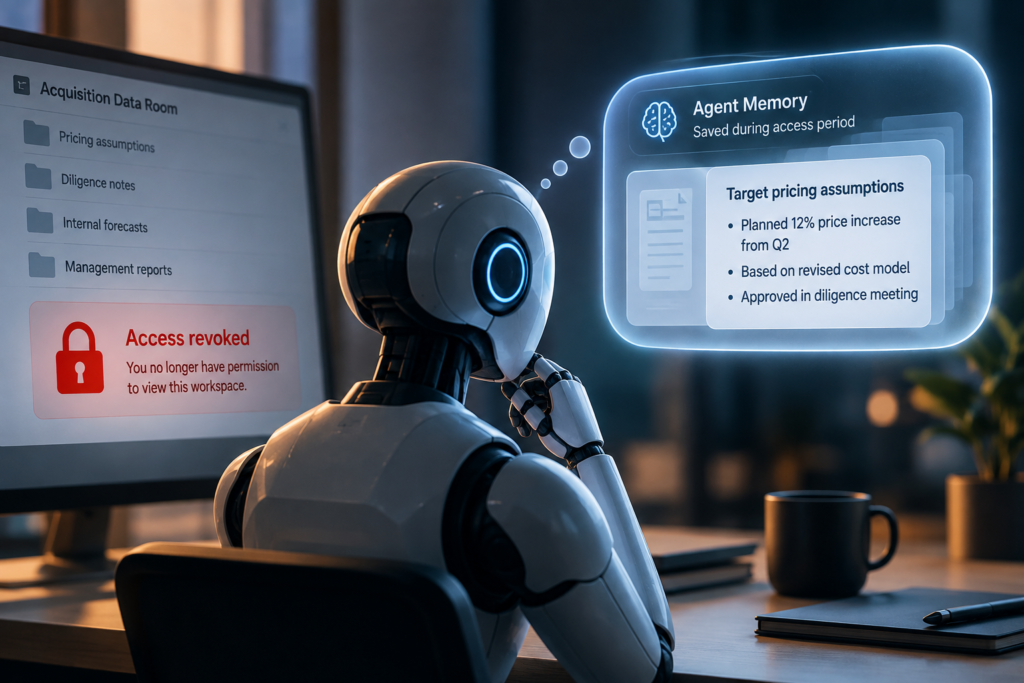
AI agent memory permission expiry creates a control problem that ordinary access revocation does not solve. An agent can lose permission to a source system while retaining facts, summaries or decisions it learned when that access was still valid.
A strategy agent receives temporary access to a restricted acquisition workspace.
For three days, it can read pricing assumptions, diligence notes and internal forecasts while supporting a transaction team. The access is deliberately short-lived. On Friday evening, the permission is removed.
On Monday, the agent can no longer open the workspace.
But during the earlier sessions it stored a summary of the target’s pricing assumptions in long-term memory.
The permission expired.
The remembered information did not.
Access control usually governs the next request to a resource. Agent memory can preserve state created by an earlier request and make it available again without rereading the original source.
Temporary access can create durable agent state
Enterprise identity systems are becoming better at giving agents bounded permissions.
Microsoft Entra Agent ID, for example, supports delegated permissions when an agent acts on behalf of a user and application permissions for autonomous activity.
Persistent memory is evolving separately. Amazon Bedrock AgentCore Memory can retain information across interactions so it remains available beyond the session in which it was first encountered.
That is useful precisely because the agent does not have to reconstruct everything from the source during every invocation.
It also creates a different control problem.
If information entered memory while the agent had legitimate access, later recall may come from that memory store rather than from the original application, repository or database.
Revoking source access therefore leaves another question behind:
Should the agent still be allowed to recall what it learned then?
Revocation needs to reach derived memory
Traditional permission revocation has a relatively clear effect.
Remove the user or application from the resource, and subsequent access requests should fail.
With persistent memory, a summary, extracted fact or previous decision may remain available elsewhere after the source itself becomes inaccessible.
Current memory architectures make that separation visible. Amazon Bedrock AgentCore gives stored memory its own retention configuration, independently of the permissions governing the system from which the information was originally obtained.
The broader control point is straightforward: memory lifecycle and permission lifecycle are separate controls unless the application deliberately connects them.
A project agent may receive data-room access for one engagement. A support agent may inspect a sensitive customer record during an escalation. An HR agent may temporarily see compensation information while preparing an approved analysis.
Each permission can have a defined end date.
Derived information created during that window needs its own treatment once the window closes.
A memory needs more than a timestamp
Age alone says little about whether remembered information remains appropriate to use.
A fact stored yesterday may already sit outside its permitted context. Another stored months ago may still be valid for recall.
Sensitive memory therefore needs enough source-authorization lineage to preserve the conditions under which it was created.
That may include the source system, the user or agent authority involved, the scope or task that justified access, and any expiry or lifecycle condition attached to that access.
The purpose is not to reproduce the entire identity token inside the memory store. It is to prevent a remembered fact from becoming permanently detached from the permission context that allowed the agent to learn it.
Return to the acquisition example.
A memory saying that the target plans a particular price increase may have been created legitimately during diligence. Once the transaction closes, is abandoned or moves to a different team, the original access arrangement may no longer apply.
If the memory retains only the fact, there is little basis for deciding whether recall is still appropriate.
If it also retains the provenance of the authorization that produced the fact, later use can be evaluated against that context.
Recall is another authorization moment
When an agent recalls persistent context in a later session, it introduces stored information into a new task.
The user, identity, purpose and permissions surrounding that task may differ from the conditions under which the memory was captured.
Google’s Memory Bank documentation illustrates this retrieval boundary by scoping persistent memories to identities and providing controls around access to those memory scopes.
That makes recall a point at which authorization can be reconsidered.
Some memories may remain generally available. Others may require a matching project or case context, a current user entitlement, the originating permission to remain valid, or renewed approval before the information enters the agent’s working context.
The objective is to prevent a past authorization event from becoming an indefinite future authorization.
This does not require every permission change to trigger wholesale memory deletion.
What matters is whether the remembered information remains eligible for use in the new context.
Permission expiry should change what memory can be recalled
Memory governance often focuses on retention duration: how long information should be stored.
Access control needs another decision as well: whether stored information may still be used.
A useful architecture can separate retention from recall eligibility.
A memory may remain stored for audit, continuity or operational reasons while being blocked from future agent interactions after the originating permission expires. Another implementation may revalidate the current identity before retrieval. For some categories of information, deletion may still be the appropriate response.
The policy will depend on the data and workflow.
What matters is that a time-bounded permission should not silently create memory with an unlimited right of reuse.
Identity systems are increasingly capable of answering whether an agent may access a resource now.
Persistent memory adds another question:
Should the agent still be able to use something it learned when that answer used to be yes?
An agent’s permission can expire in an instant.
Its memory needs a lifecycle that notices.